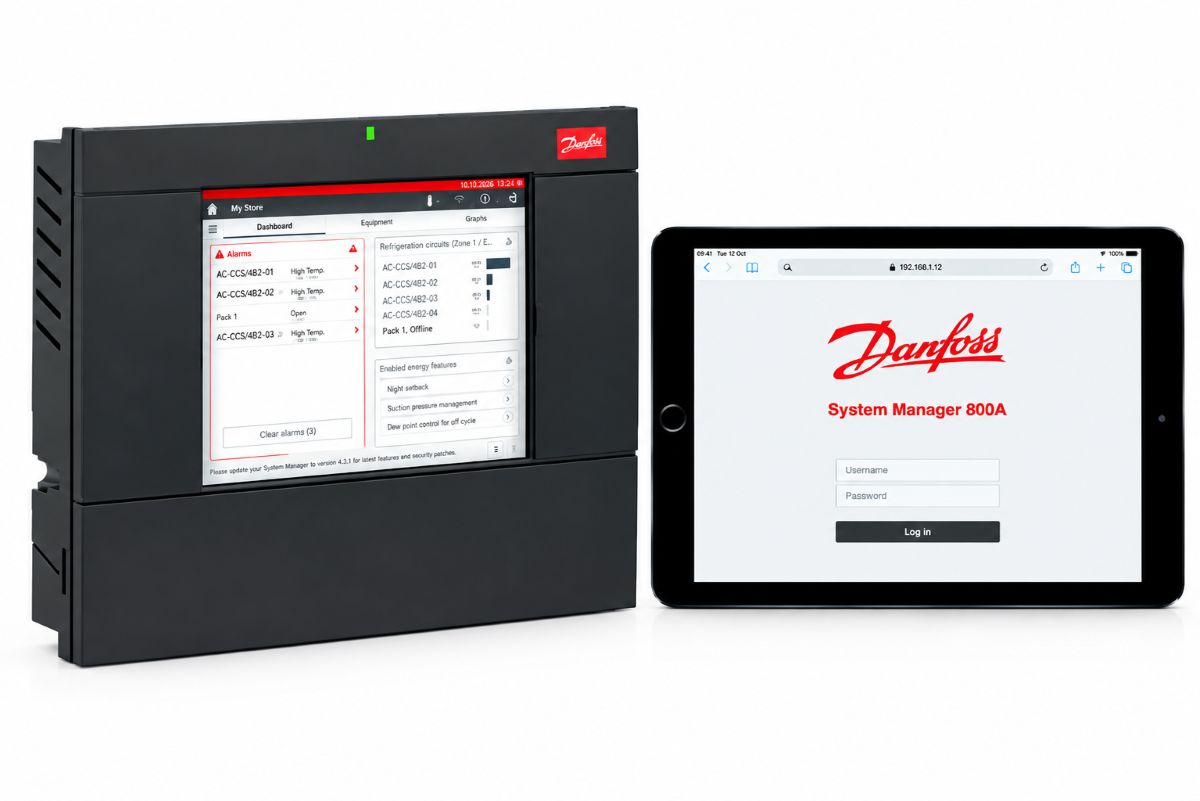
During the night of October 11 to 12, a cyberattack took control of two models of Danfoss regulators which control cold rooms and refrigerated furniture in supermarkets and hypermarkets and increased the temperatures
The CERT-FR (French Computer Emergency Response Team), L’French government entity ensuring the operational implementation of the function of digital systems defense authority of interest for the nation within the ANSSI (National Agency for Information Systems Security), gave the alert on the morning of October 12, revealing a ‘security incident targeting Danfoss AK-SM and AK-SC series controllers“. THE hackers hijacked a legitimate function of these regulators : there defrost management.
THE AK-SM and AK-SC regulators have an administration interface accessible from an internet browser. This interface also sends alerts to maintenance managers in the event of a malfunction. There internet connection was used to modify the defrost control parametersconstraining the refrigerated cabinets has increase their defrost temperature to 50°C and maintain it for several hours. What has ruined the contents of the refrigerated cabinets. Seized of the case, the Paris Prosecutor’s Office even mentions the outbreak of fires caused by these high temperatures maintained for a long time.
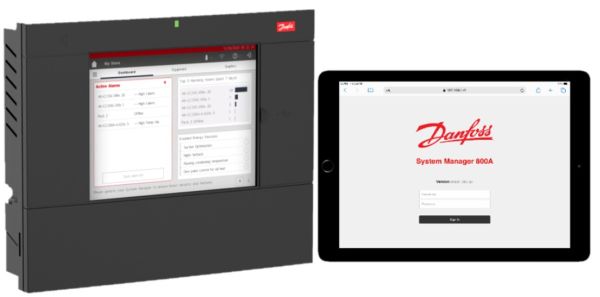
The software of the AK-SM 8xxA controller had vulnerabilities. Danfoss has published corrections, which have not been implemented in the field. © Danfoss
Vulnerabilities identified
In March 2025, Danfoss released a new version (4.2) of the software for controlling AK-SM 8xxA controllers. Called CVE-2025-41450, the patch modified an authentication mechanism that could allow certain protections to be bypassed. On August 1, 2025, Danfoss released a new version (4.3.1) to correct two new vulnerabilities, called CVE-2025-41451 and CVE-2025-41452. They allowed an actor identified by the system to order the regulator to execute commands transmitted to them. Claroty TEAM82, a specialist in the defense of industrial, healthcare and commercial networks, has published two analyzes of vulnerabilities of Danfoss regulatorsidentifying a high threat in the case of AK-SM8xxA regulators if they are equipped with software older than the version, as well as a medium threat on the same regulator.
Moreover, in the list of vulnerabilities identified by Claroty TEAM82we are faced with a list of the big names in the industry: Trane, Schneider-Electric, Johnson Controls, Copeland, Metz Connect, Samsung, ABB, etc. Claroty TEAM82 researchers identified 2,765 AK-SM 800A controllers directly accessible via the internet and on August 9, 2026, they published an alert with the prescient title “Freeze the controller, Defrost the food” describing almost exactly what just happened.
Danfoss is exhibiting at the IBS Show in Paris, October 14 and 15. This will be an opportunity to ask them for additional information.
Considerable damage
Several supermarket chains were affectedwhich translates to approximately 500 stores attacked : Leclerc, Intermarché, Monoprix, Système U, Carrefour, Netto, … The list continues to grow. The damage, according to the Paris Prosecutor’s Office, would reach millions of euros.
For now, theimage of Danfoss is not achieved: the company successfully issued a bond of 500 million euros on October 12, with a maturity of 5.5 years with a yield of 4.361%. The issue was largely oversubscribed by investors, recording overall demand of nearly €3 billion. The question of responsibility still arises.
Depending on the chain, the stores and their technical equipment in independent networks belong to their operators. There maintenance of cold systems is entrusted to refrigeration specialists. Their role is mainly to intervene in the event of breakdowns and to ensure regular maintenance. It is not certain that they are trained in the vulnerability issues of the communications solutions available to these facilities, or even that this issue is included in their contracts.
Danfoss has published patches, warned about the risks associated with end-of-life equipment, but probably not with enough force. Several generations of controllers have presented vulnerabilities and many affected products remain in operation: the message has not reached decision-makers. The European CRA (Cyber Resilience Act), which comes into force on January 1, 2027, could force everyone to pay attention to cybersecurity. © Danfoss
/ © Danfoss